Preemptive intelligence for telecommunications networks
Telecommunications providers sit at the centre of national infrastructure, and adversaries know it. Lupovis captures real attacker activity across the exposed services and network edge that telcos rely on, then turns it into the context your security teams need to act before impact.
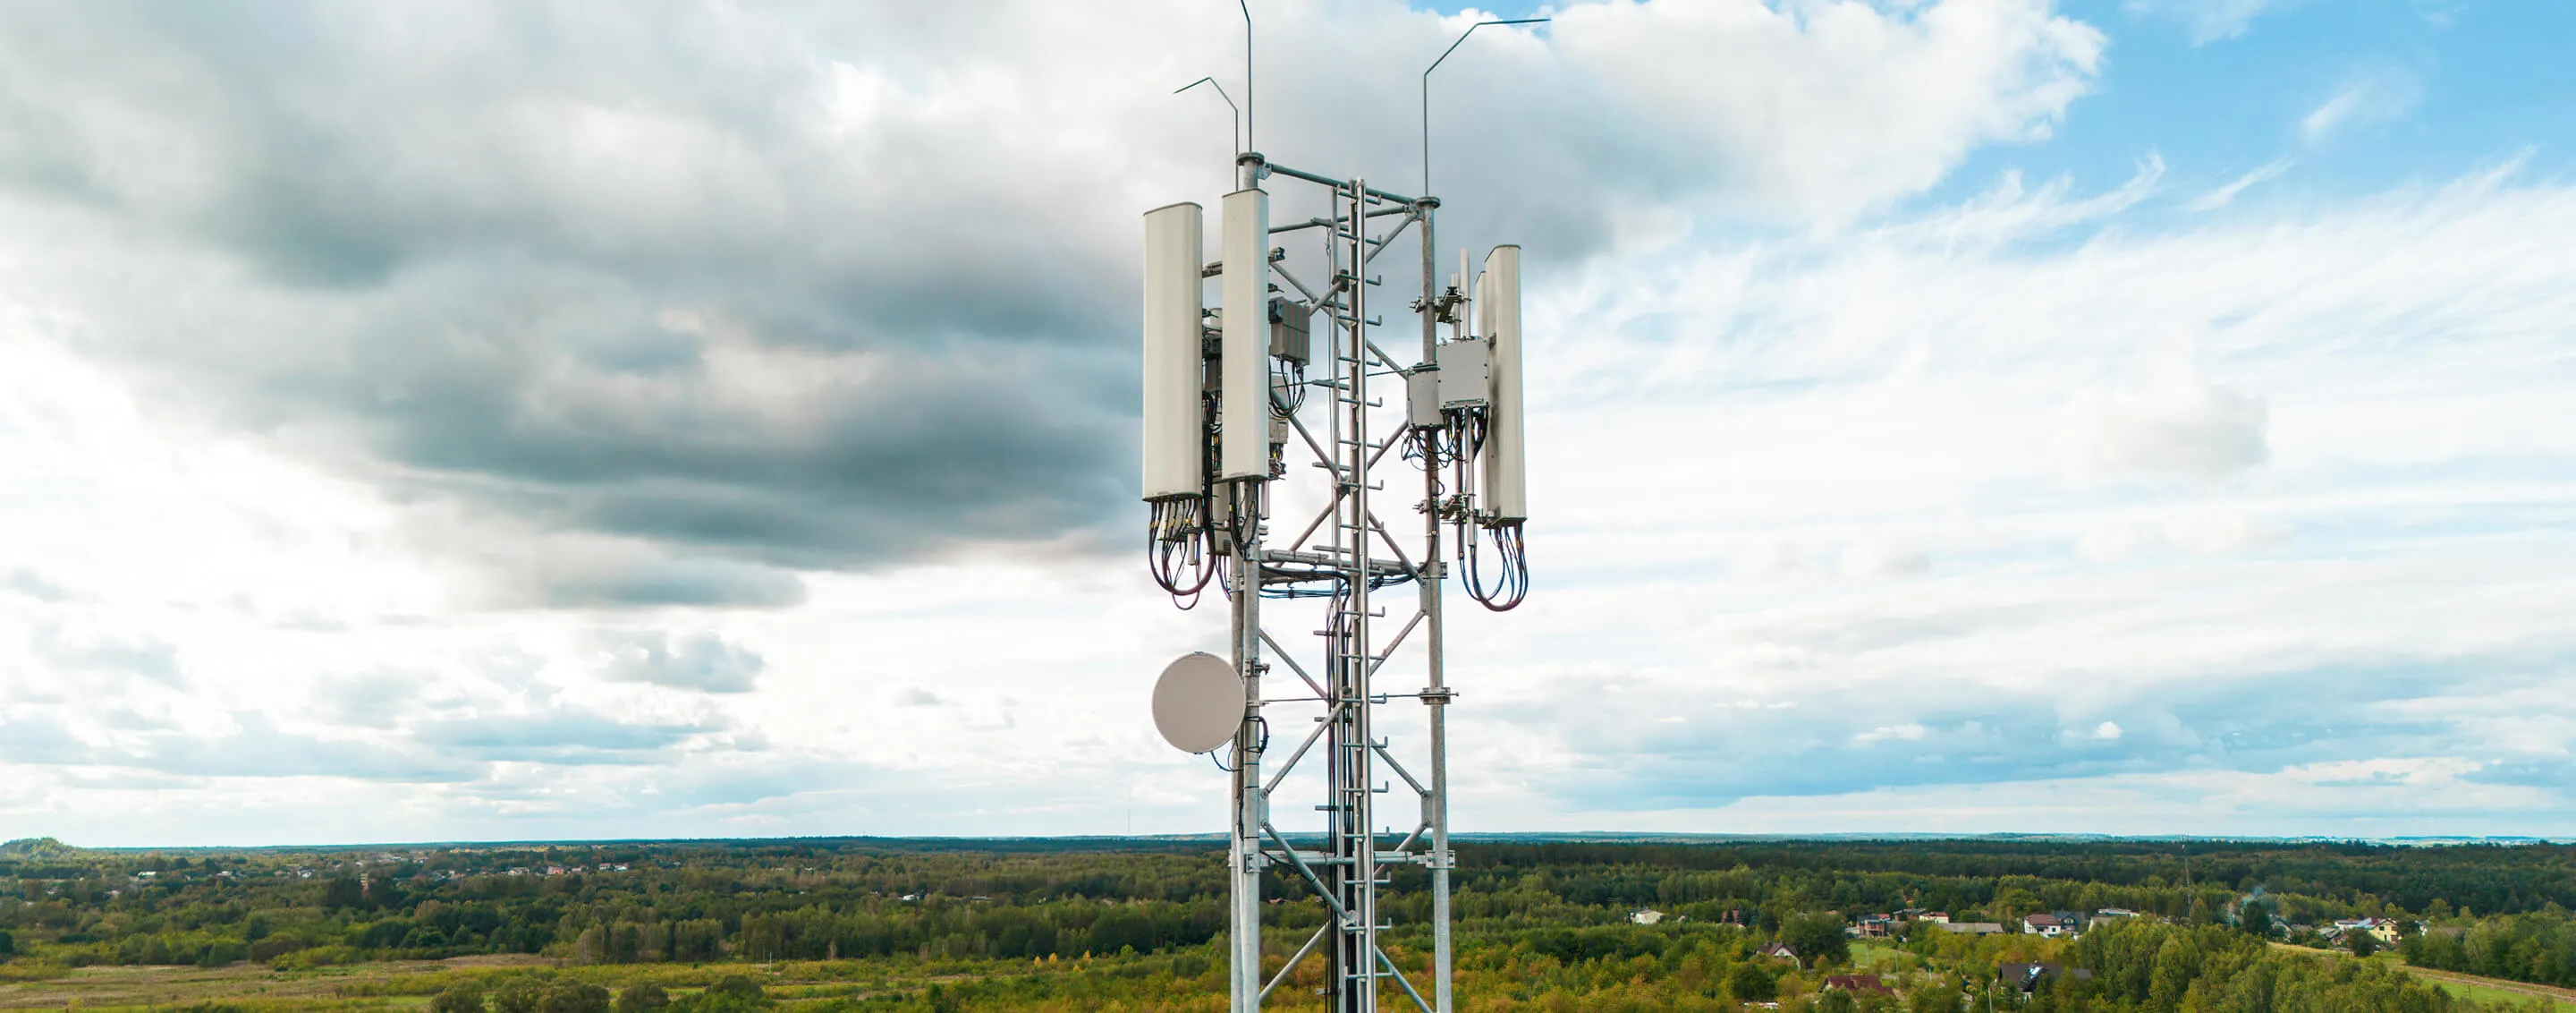
Where telecommunications sits in the threat picture.
Reconnaissance on the network edge
Sustained probing of remote access, VPN concentrators, edge routers, SD-WAN, and internet-facing management interfaces.
Attacks on identity systems
Coordinated login attempts and enumeration against SSO portals, RADIUS, and authentication gateways.
Behaviour linked to known clusters
Infrastructure overlap with clusters known for long-running interest in the telecommunications sector.
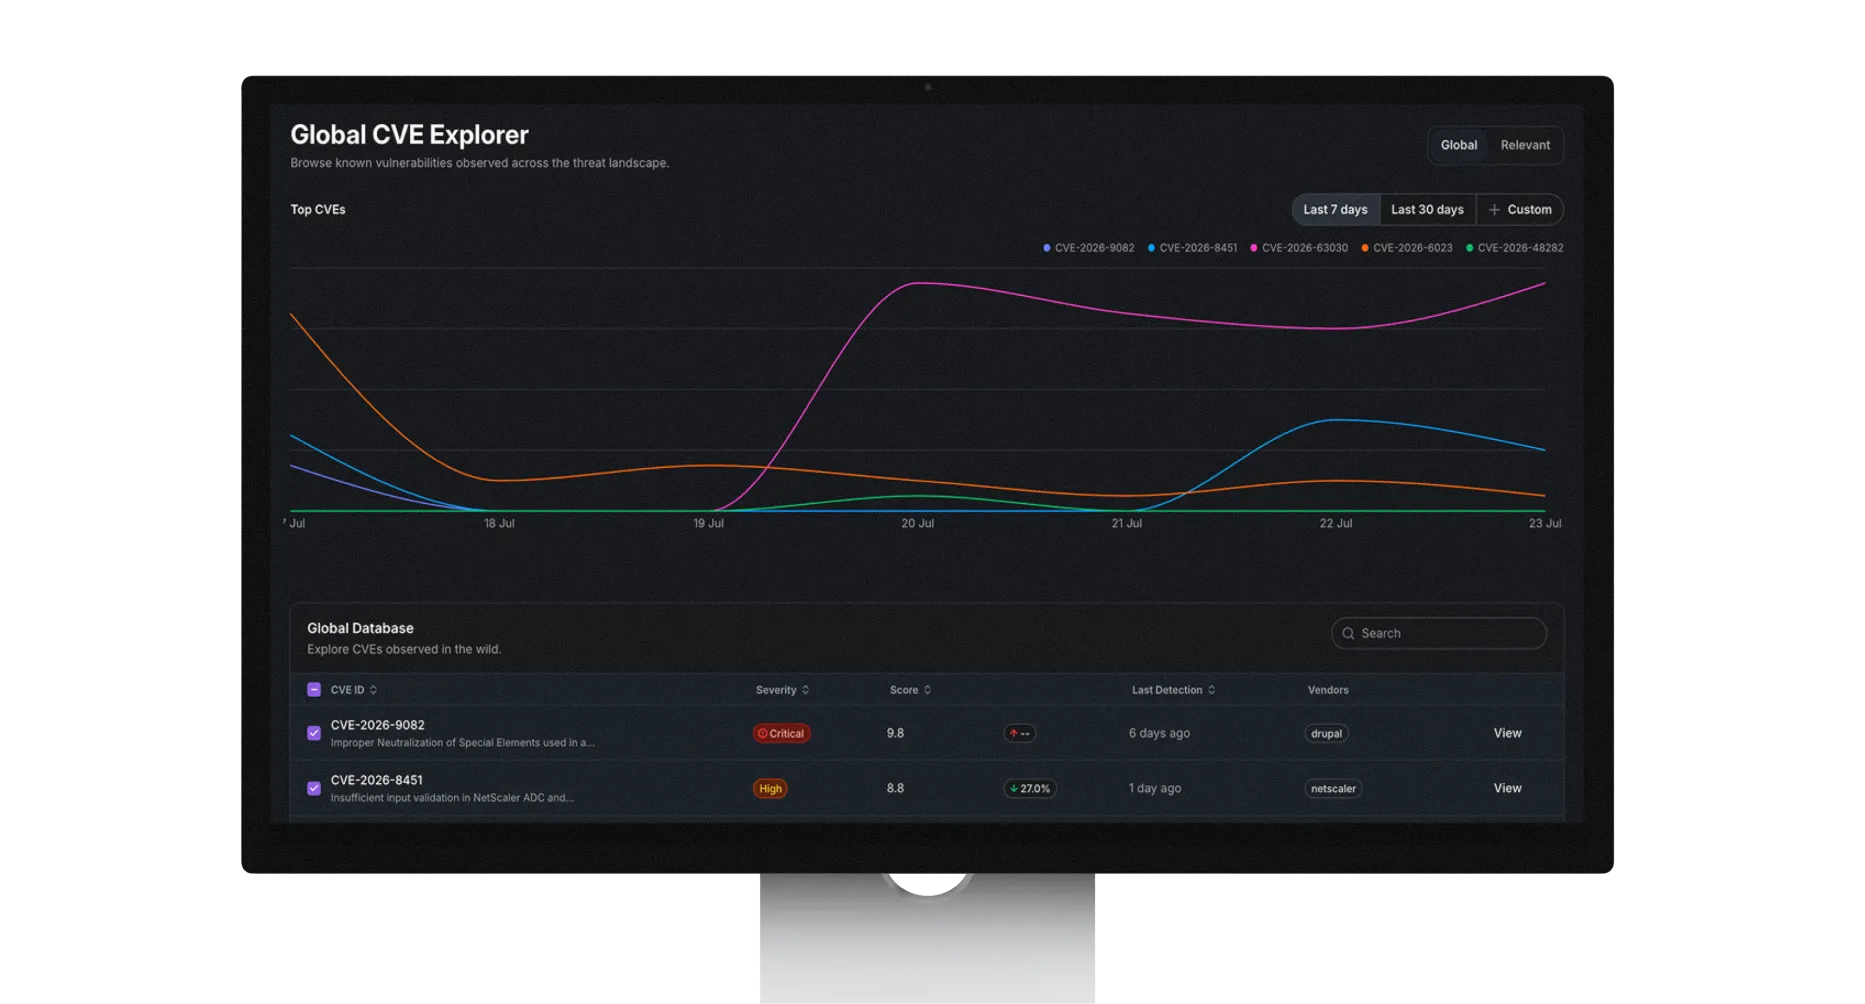
Probing before CVEs go public
Vendor-aligned activity that consistently precedes public advisories, giving your team a real lead window.
Trusted by telecommunications leaders and their security partners

“Lupovis helped us detect a threat within our telecommunications infrastructure and gave our team the context needed to investigate it. By connecting suspicious IP activity with threat intelligence, we gained a clearer understanding of what we were dealing with and where to focus our attention. That visibility helped us move from identifying suspicious activity to assessing the threat it posed to our infrastructure. For a security team protecting telecommunications services, this is a valuable outcome: clearer evidence to guide investigations and better informed decisions about how to respond.”

“We deploy the Lupovis platform to enhance all of our Micro-SOC customers, enriching threat intelligence and accelerating incident response to stop threats before a breach”
"Lupovis’ active decoy technology has allowed us to effectively protect and validate the network hygiene of a number of satisfied partners. Their responsive and flexible approach has enabled us to deploy effectively and efficiently across complex network environments and the high quality, detailed information provided by their platform makes contextualising any potential threat an easy and reliable process."

Attacker activity clusters before CVEs go public.
US carriers confirmed compromised in Salt Typhoon
9
Volt Typhoon dwell time in western telecoms networks
Up to 5 years
Edge and routing devices unpatched at any given time
40%
Built for telecommunications security teams.

See what is already targeting your network
Get a 30-minute walkthrough with the Lupovis team. We will show you attacker activity already observed against telecommunication providers like yours.