See the attack before it reaches public services
Attackers move faster than advisories, procurement cycles and patch windows. Lupovis shows you the hostile infrastructure, exploited vulnerabilities and adversary activity aimed at public sector technology as it happens. Your defenders then have the evidence to block, patch and hunt before an attack can disrupt services.
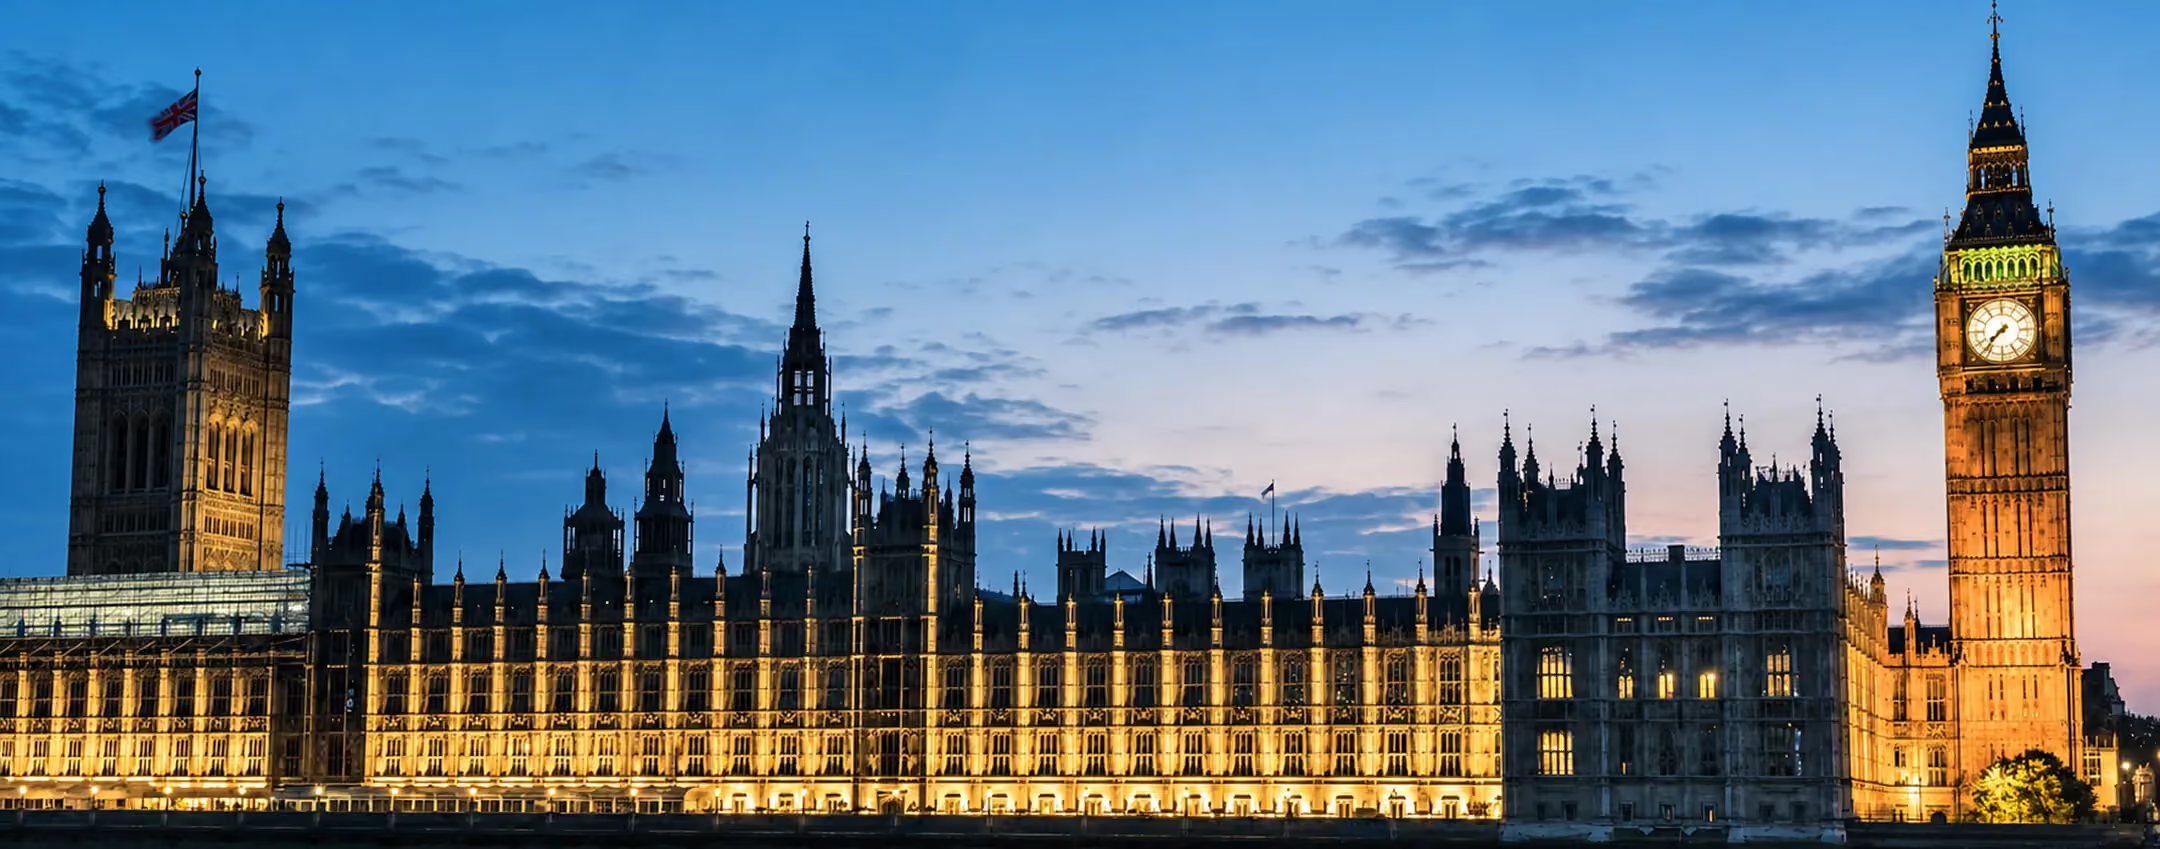
Public services are already being mapped, probed, and exploited.
State-aligned
targeting
See the infrastructure and techniques used to map government, defence-adjacent, and critical public services before access is attempted.
Exploitation before prioritisation
Identify the CVEs attackers are using now, including activity that appears before public advisories and KEV updates.
Ransomware and access brokers
Track infrastructure used to probe councils, healthcare, education, and shared suppliers for exposed edge systems and credentials.
Politically motivated disruption
Detect the infrastructure behind politically timed DDoS, defacement, and disruption campaigns before public-facing services are affected.
Trusted to protect public services
Generic internet noise is not intelligence. Intent is.
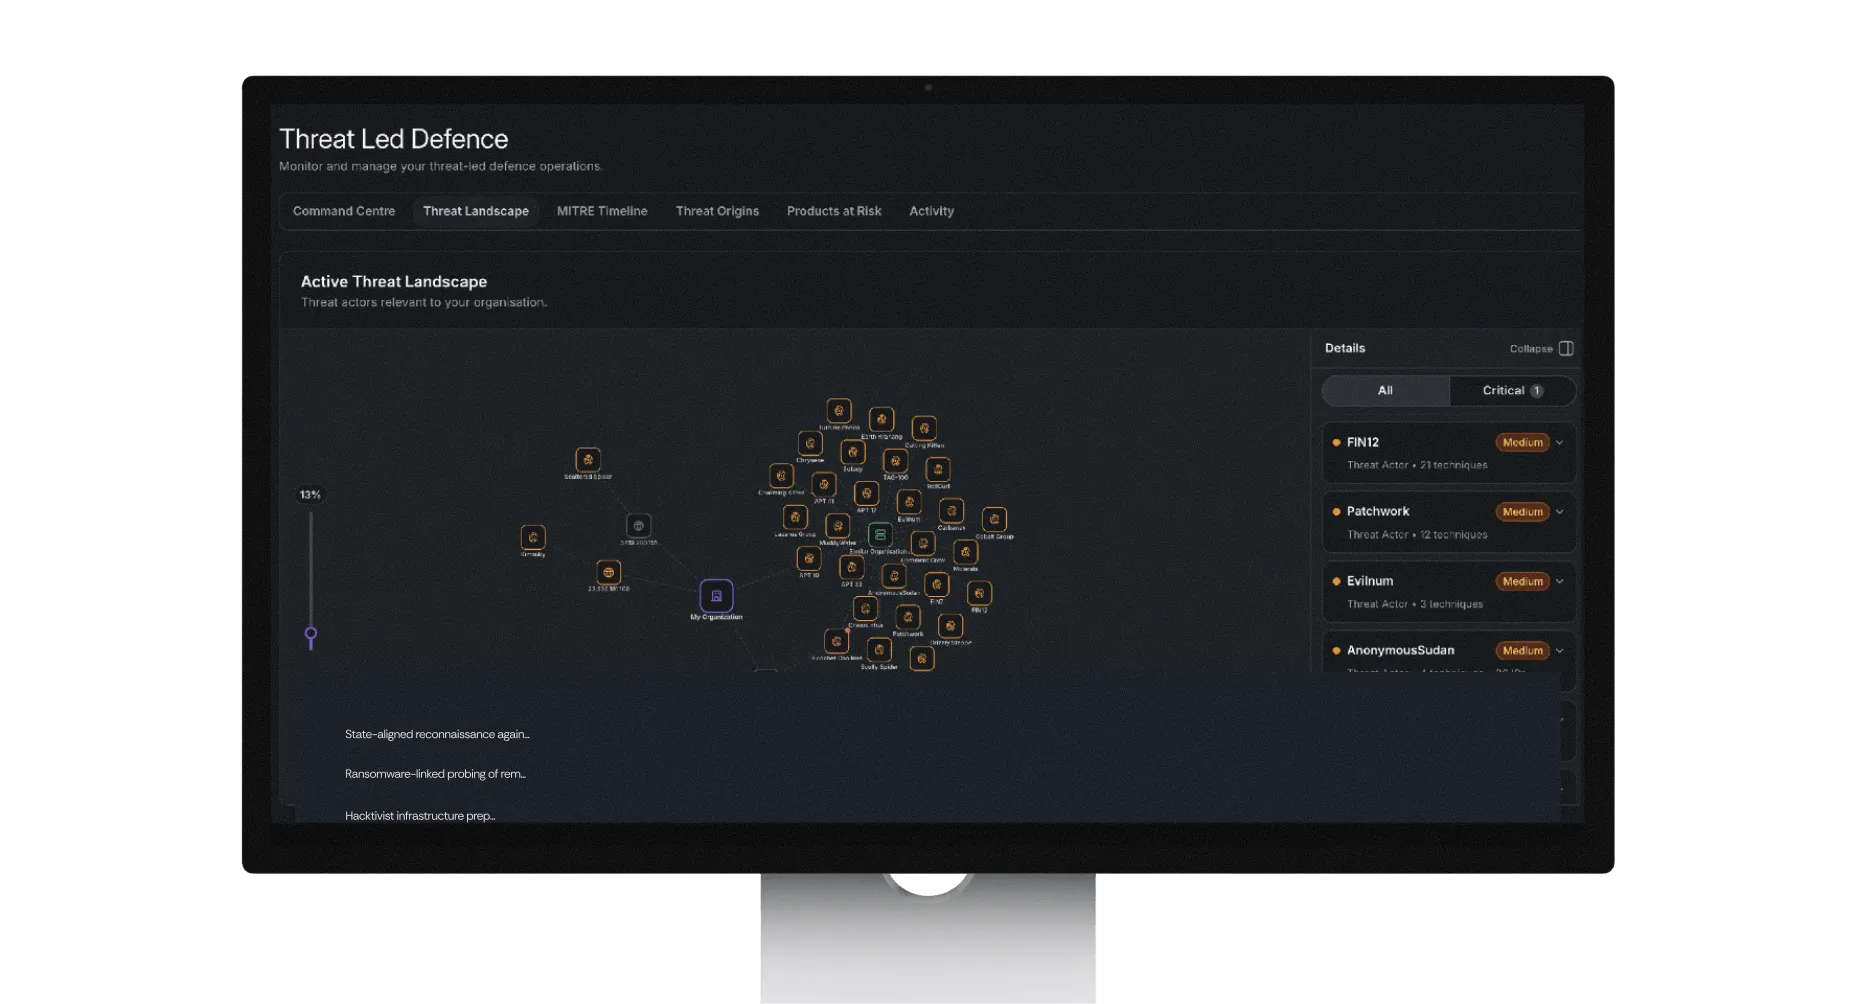
You don’t need another feed of internet scans. You need to know who is targeting public-sector technology, what they’re exploiting, whether your organisation is exposed, and what to do next. Lupovis combines real-world attacker activity, deployed decoys, and organisation-specific telemetry to turn hostile activity into clear, actionable intelligence.
Who is targeting our organisation, sector, suppliers, or technology stack?
Which vulnerabilities are attackers exploiting right now?
Which infrastructure should we block or investigate immediately?
What evidence should our SOC hunt for internally?

Attacker activity clusters before CVEs go public.
Ransomware attacks on UK councils and public bodies in the past two years
70+
Average recovery cost for a major public sector breach
£10m+
Share of local authorities that reported a cyber incident last year
1 in 5
Turn hostile activity into action before impact.
Know when attention turns toward you
Patch what is being exploited now
Block hostile infrastructure faster
Hunt with evidence, not assumptions
Identify adversaries probing your organisation, sector, suppliers, and the technology your services depend on. Separate general scanning from activity that demands immediate action.
Prioritise vulnerabilities using live exploitation evidence, not theoretical severity alone. Move actively exploited edge technology to the top of the queue before KEV or vendor guidance catches up.
Push high-confidence attacker infrastructure into SIEM, SOAR, firewalls, and blocklists. Reduce exposure while investigations and remediation are still underway.
Turn observed payloads, TTPs, malware, and infrastructure into targeted hunting hypotheses and detection content for your SOC.
Built for public-sector security teams.

The attacker is already moving. See them first
In 30 minutes, we will show you the adversary infrastructure, exploited vulnerabilities, and targeting signals Lupovis is observing across public-sector environments now. No generic threat-feed tour. Just the evidence your team can act on.