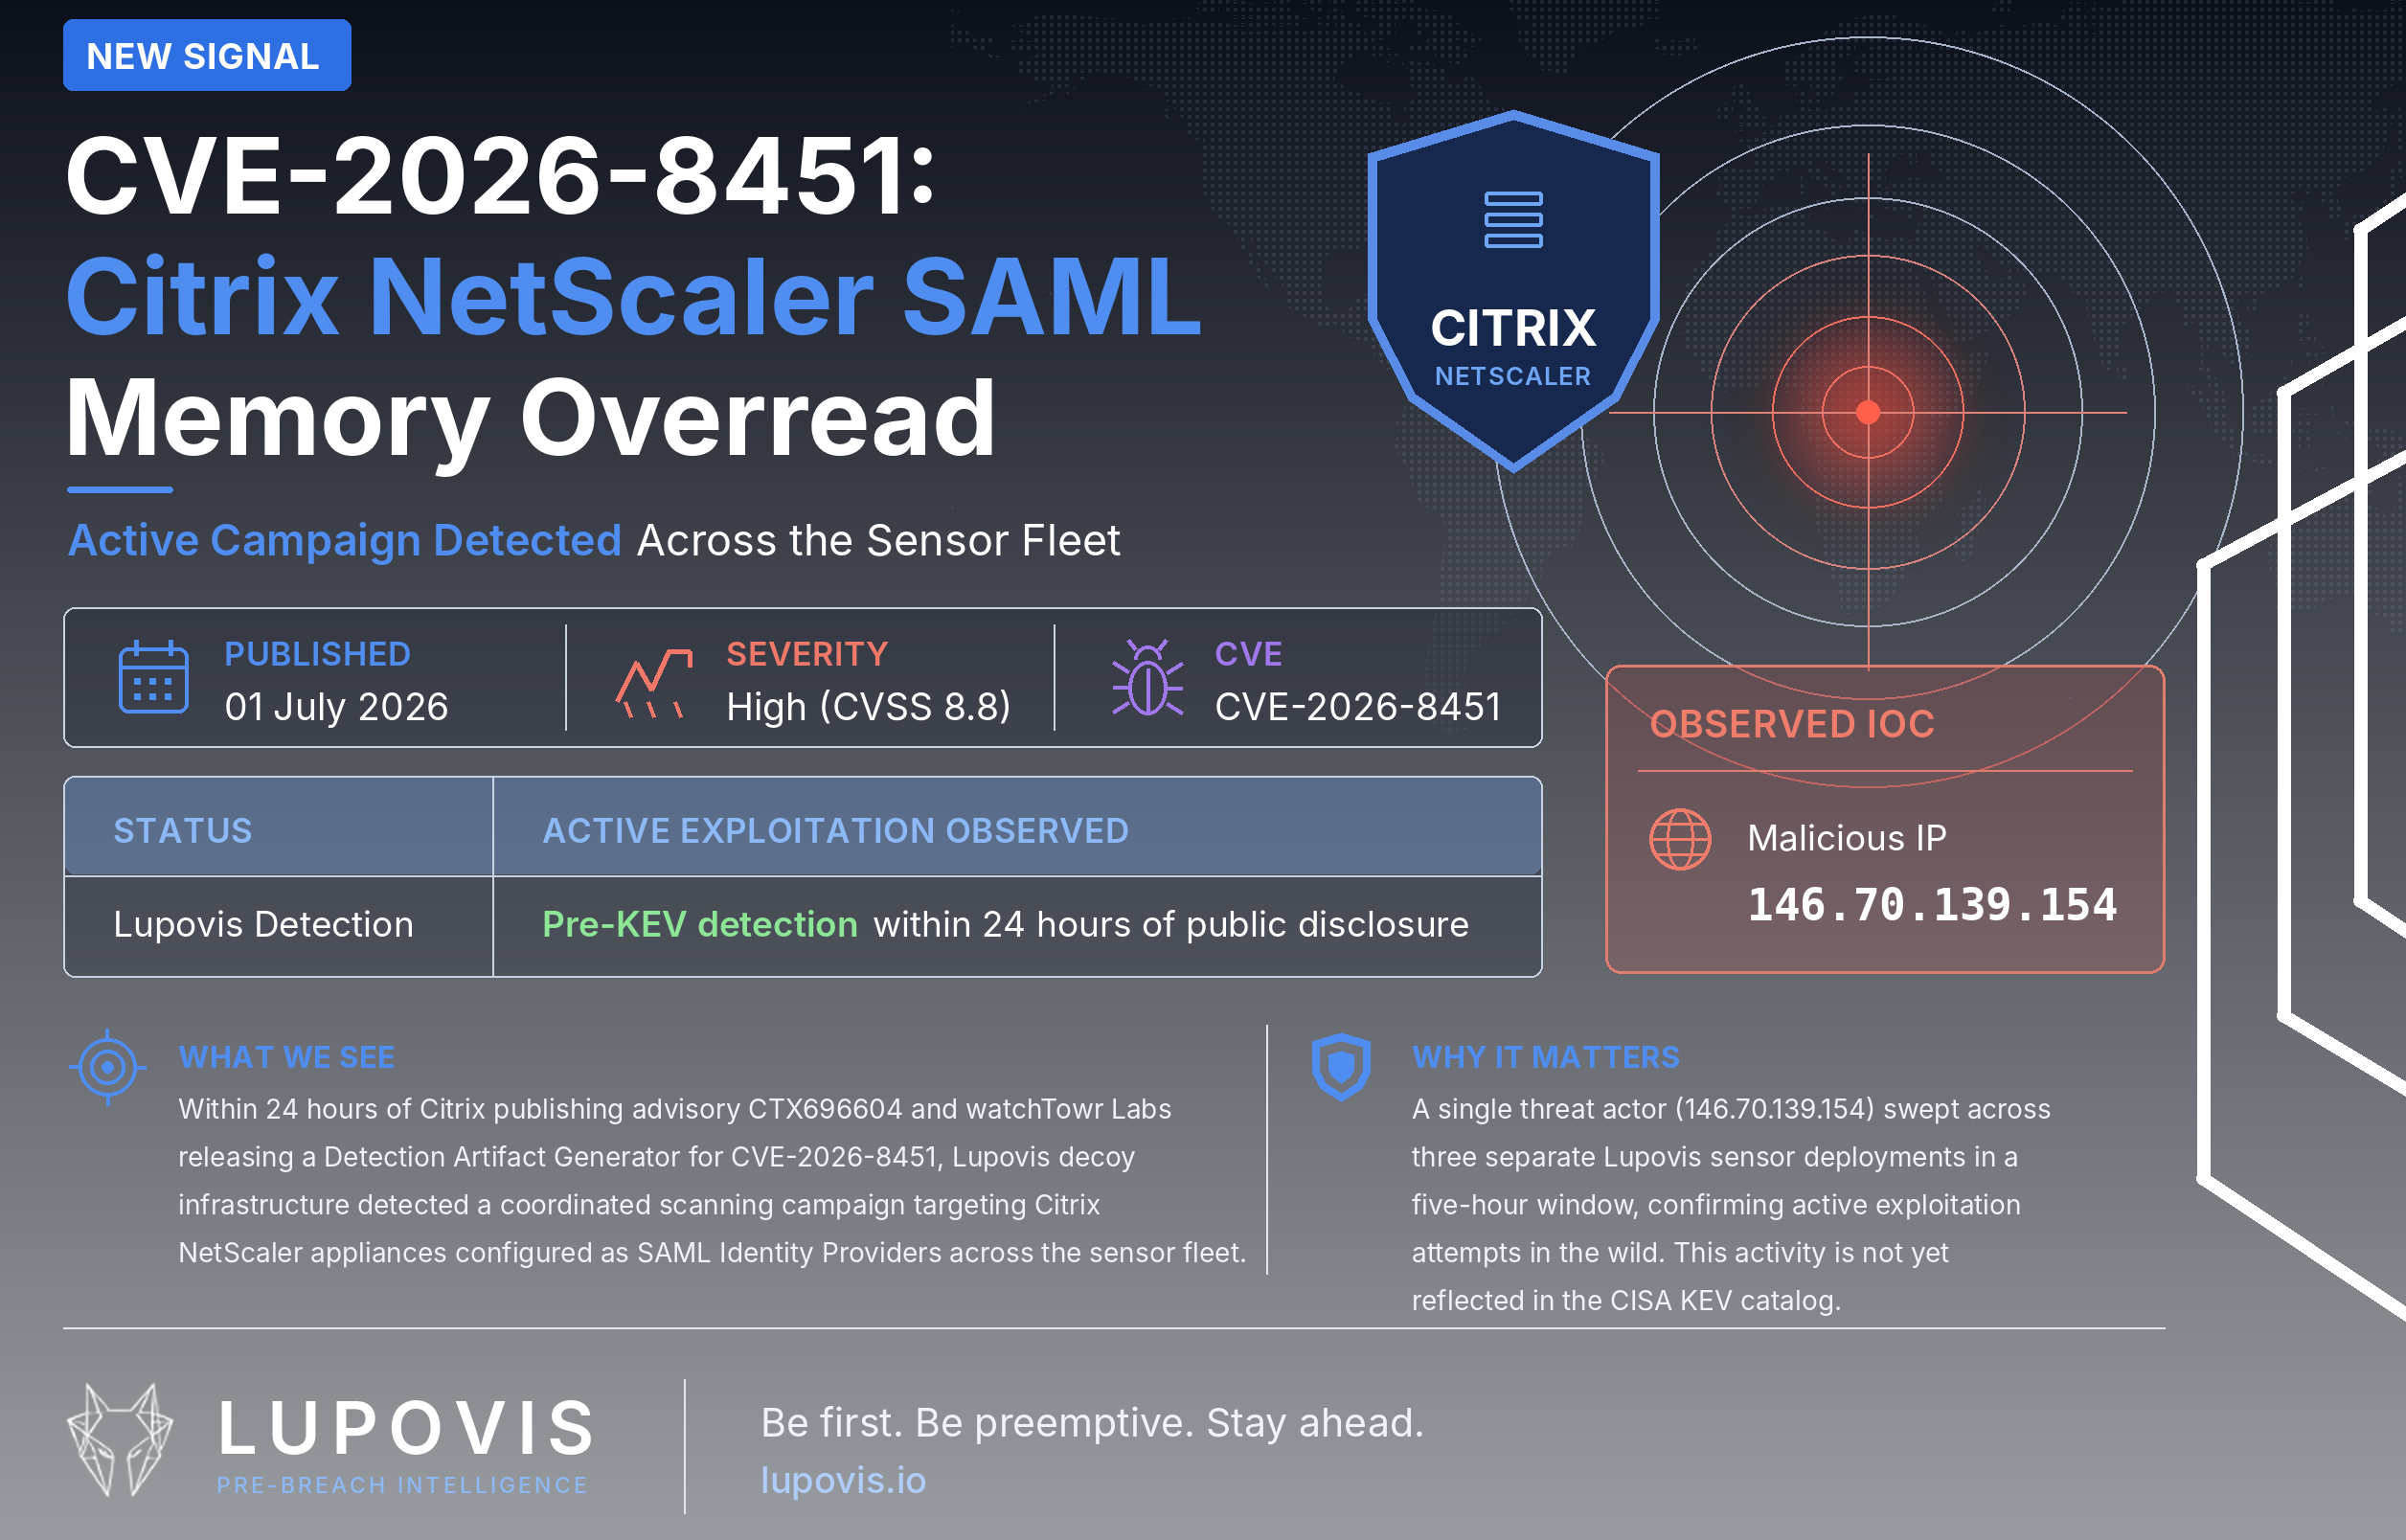
CVE-2026-8451: Citrix NetScaler SAML Memory Overread

Active Campaign Detected Across the Sensor Fleet
Published:
01 July 2026
By:
Xavier Bellekens
Severity:
High (CVSS 8.8)
CVE:
CVE-2026-8451
Summary
Within 24 hours of Citrix publishing advisory CTX696604 and watchTowr Labs releasing a Detection Artifact Generator for CVE-2026-8451, Lupovis decoy infrastructure detected a coordinated scanning campaign targeting Citrix NetScaler appliances configured as SAML Identity Providers across the sensor fleet.
A single threat actor (146.70.139.154) swept across three separate Lupovis sensor deployments in a five-hour window, delivering a confirmed CVE-2026-8451 exploitation payload. This activity is not yet reflected in the CISA KEV catalogue.
Vulnerability Background
CVE-2026-8451 is the latest in the CitrixBleed class of memory disclosure vulnerabilities – a recurring pattern of memory management failures in Citrix NetScaler appliances first identified in CVE-2023-4966 and subsequently rediscovered across multiple successive CVEs (CVE-2025-5777, CVE-2025-12101, CVE-2026-3055).
The vulnerability exists in NetScaler’s custom XML parser used to handle SAML AuthnRequest documents. The parser fails to correctly terminate unquoted XML attribute values when followed by a newline character, causing it to read past the buffer boundary. Arbitrary memory content is then returned to the attacker in the NSC_TASS cookie in the HTTP response.
Key facts:
- Unauthenticated – no credentials required
- Requires NetScaler to be configured as a SAML IdP (non-default)
- Affected: NetScaler ADC and Gateway 14.1 before 14.1-72.61; 13.1 before 13.1-63.18
- Disclosed: 30 June 2026 (CTX696604)
- PoC: watchTowr Detection Artifact Generator published same day as disclosure